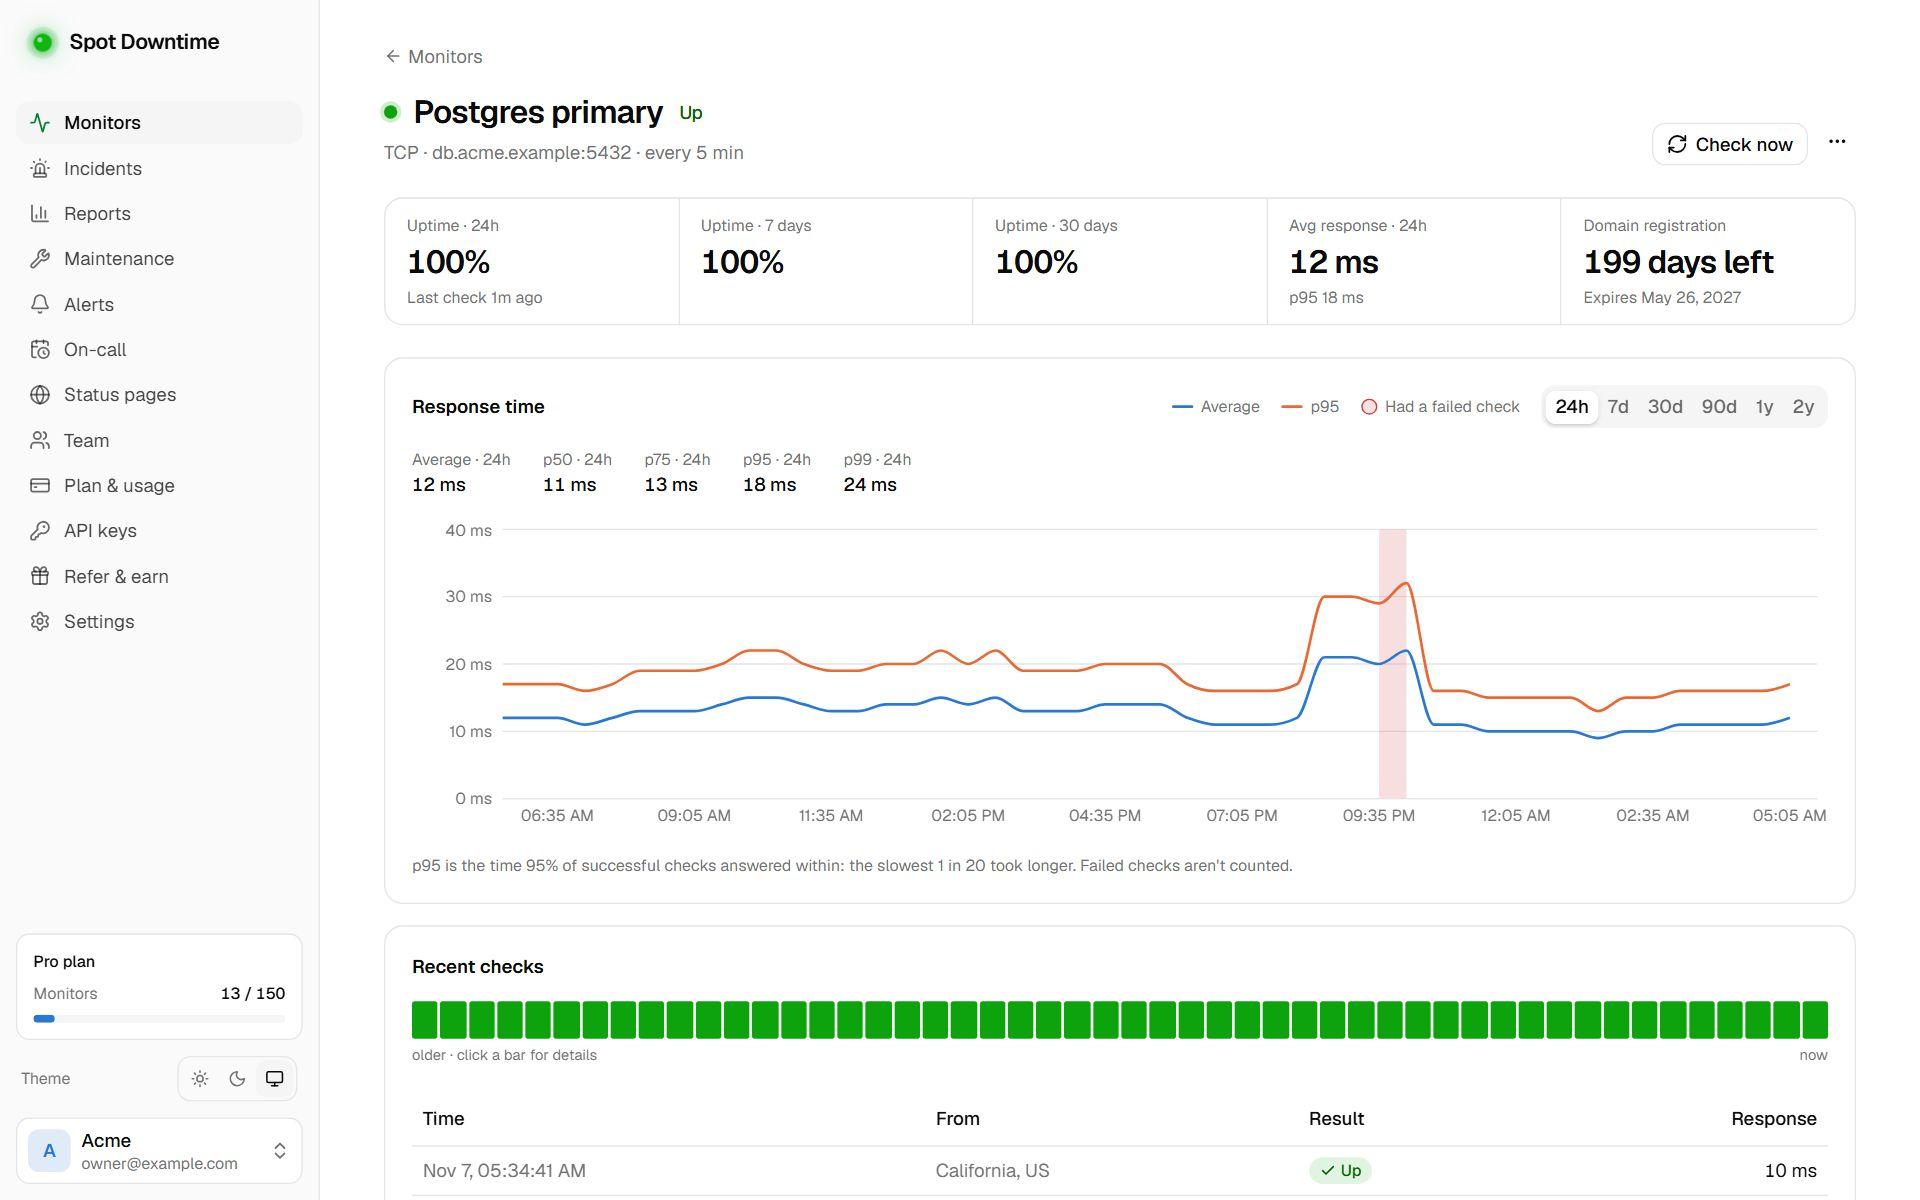
What is TCP port monitoring?
Much of what keeps a product running isn't a web page. Databases, mail servers, caches, message brokers, SSH and game servers all listen on a TCP port. A TCP port monitor opens a connection to that host and port on a schedule. If the connection is refused, times out or the host can't be found, the monitor goes down and your team is alerted.
It works with any service that accepts TCP connections, on any port from 1 to 65535, with no agent to install and no credentials to share.
What a port check tells you, and what it doesn't
A successful connection proves the service is running, listening and reachable through your firewall. That catches crashed processes, servers that didn't come back after a reboot, broken firewall rules and DNS records pointing to the wrong machine.
It doesn't log in or run a query, so it can't tell you a database is returning wrong data. For services with an HTTP health endpoint, add an API monitor with assertions next to the port check.
Common ports to monitor
PostgreSQL on 5432, MySQL on 3306, Redis on 6379, MongoDB on 27017, SMTP on 25 or 587, IMAP on 993, RabbitMQ on 5672 and SSH on 22 are the usual candidates. Each check records how long the connection took, so the chart also shows when a service starts slowing down.
Checks come from the public internet and private addresses are blocked, so the service must be reachable from outside. If you restrict access by IP address, allow Spot Downtime's published checker addresses.