All features
API monitoring

API monitoring with JSON assertions and multi-step flows

Check that your API doesn't just respond, but responds correctly. Send any method with your headers and body, assert on the status code and the fields in the JSON response, and chain requests to test whole flows like log in, then fetch orders.

Real requests

GET, POST, PUT, PATCH, DELETE or HEAD, with custom headers such as an API key, and a JSON or text body.

Assertions on any field

Check nested values and list lengths: status equals ok, data.items.length greater than 0, error does not exist.

Clear failure reasons

Alerts say exactly what broke, for example: queue.depth should be less than 100 (got 412).

Multi-step flows

Chain up to 6 requests. Save values from a response, like an access token, and use them as {{token}} in later steps. Cookies carry over, so login flows work.

See it in Spot Downtime

The real app, with a demo team's monitors. Included on every plan, Free too.

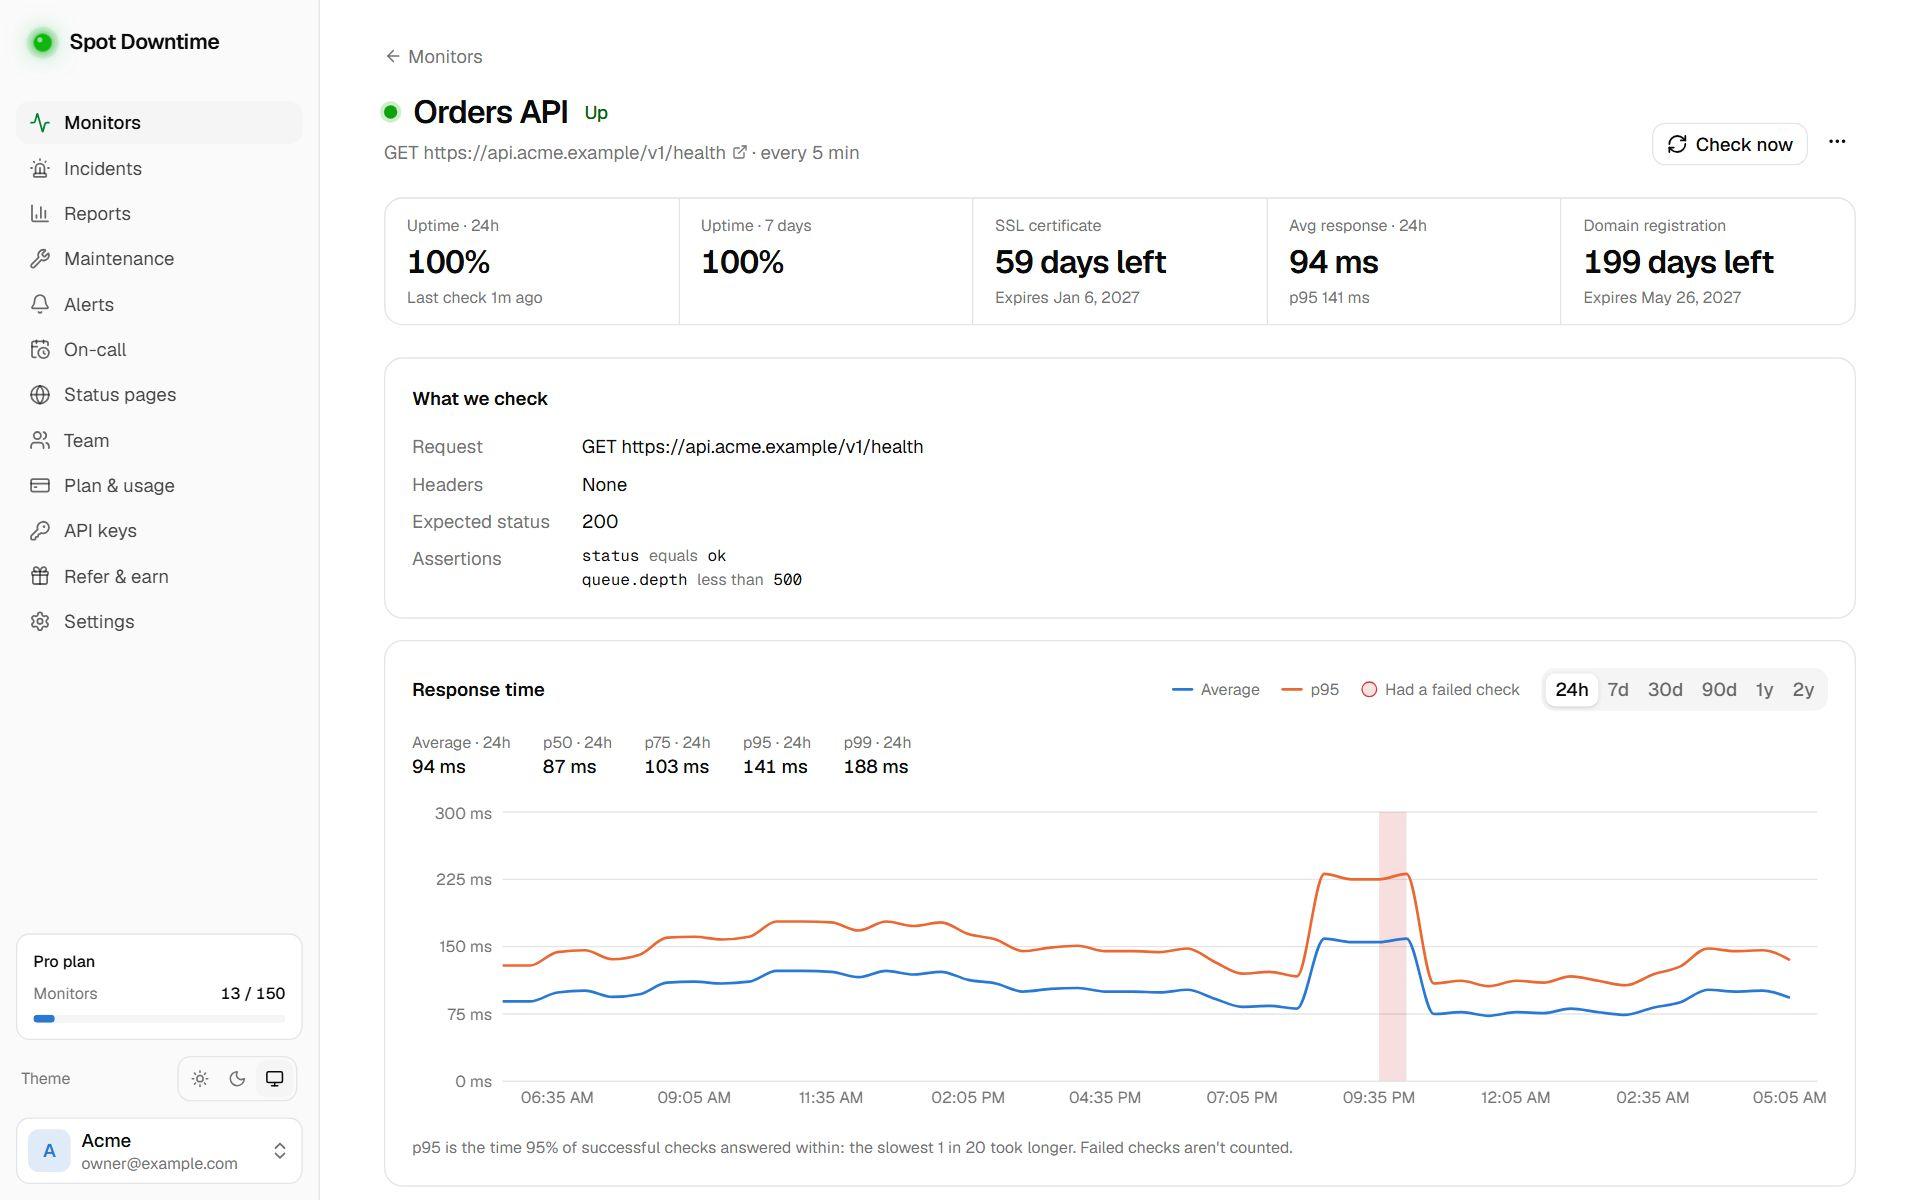
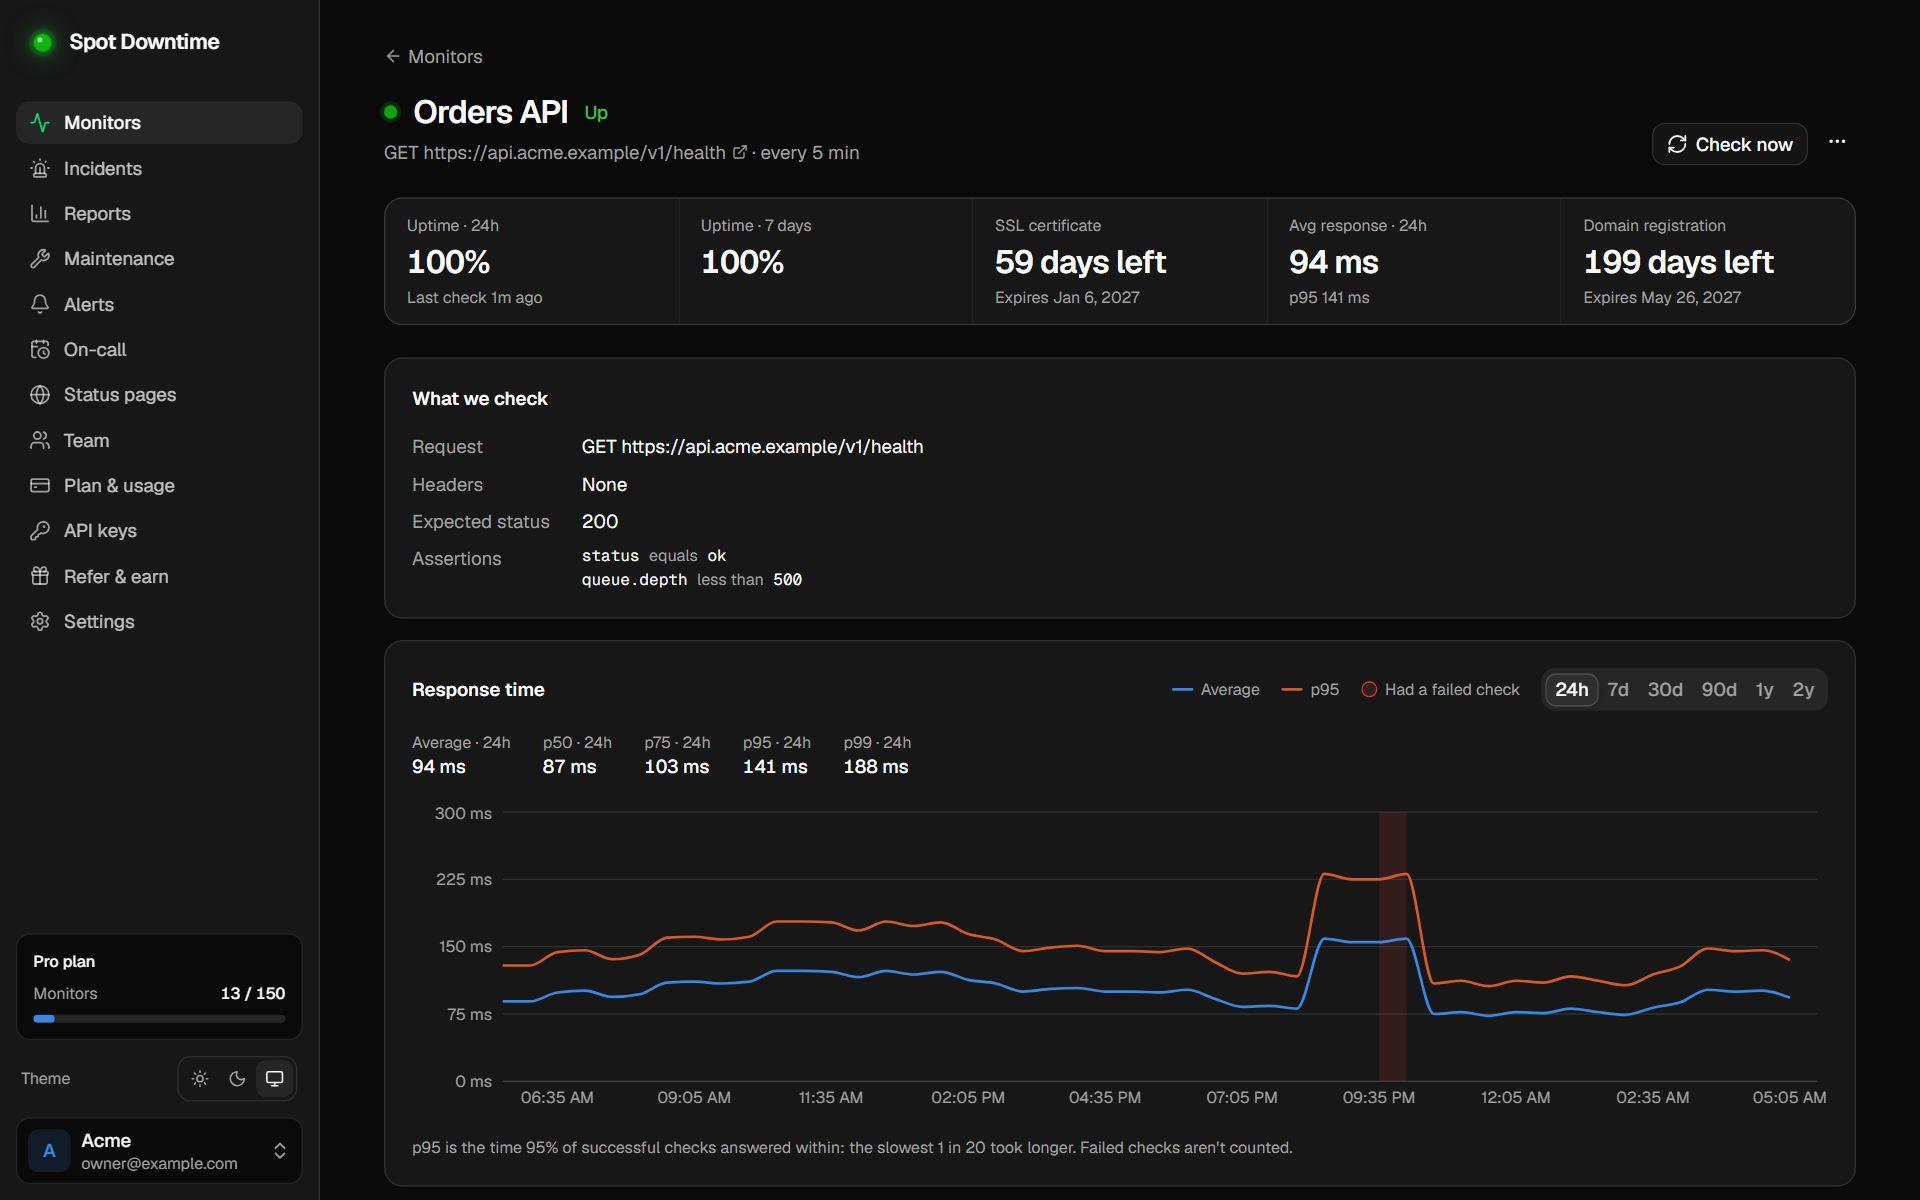
An API monitor's page with its assertions and response times
An API monitor that checks the status code and two fields in the JSON it returns.

What is API monitoring?

API monitoring sends real requests to your endpoints on a schedule and checks the responses, the same way an app or a partner integration would. It tells you when an API is unreachable, slow, returns the wrong status code, or returns data your clients can't use.

Mobile apps, single-page frontends and integrations all depend on APIs, so an API failure usually looks like “the app is broken” to customers, even while your website loads fine. Watching the API directly finds the cause faster.

Assert on the response, not just the status code

An endpoint can return 200 with an error in the body, an empty list or a stale value. Spot Downtime reads the JSON response and checks the fields you care about: status equals “ok”, data.items.length greater than 0, error does not exist. Paths use dot or bracket notation, so nested values and list items are easy to reach.

Add up to 20 assertions per monitor and set the exact status code you expect, such as 201 for an endpoint that creates something. When an assertion fails, the alert names the field, the rule and the value that came back, for example: queue.depth should be less than 100 (got 412).

Authenticated and write endpoints

Send GET, POST, PUT, PATCH, DELETE or HEAD requests with up to 20 headers and a JSON or text body. That covers bearer tokens, API keys and health endpoints that expect a POST. Use a dedicated read-only key where you can, because headers are visible to everyone in the workspace.

HTTPS API monitors also track the certificate's expiry and warn 14, 7 and 1 day ahead, and failures are confirmed from more than one region before anyone is alerted. Add cron job monitoring for background work, and a status page to keep the people who use your API informed.

How to set it up

  1. 1Click Add monitor and choose API.
  2. 2Pick the method, enter the URL, and add headers and a body if the endpoint needs them.
  3. 3Optionally set the exact status code you expect.
  4. 4Add assertions on the JSON fields that matter.
  5. 5On Starter and up, add more steps, saving values like a token from one response for the next, then save.

The details

Methods
GET, POST, PUT, PATCH, DELETE, HEAD
Assertions
equals, does not equal, contains, greater than, less than, exists, does not exist; up to 20 per monitor
Paths
Dot or bracket notation, e.g. data.items[0].id; .length on lists and strings
Headers and body
Up to 20 headers; body up to 10,000 characters
Multi-step
Up to 6 requests in order, 10 saved values per step, cookies kept between steps, 30 seconds in total
Plan
All plans, including Free; multi-step checks on Starter and up

Questions

How do saved values work in a multi-step check?
In a step, save a field from its JSON response under a name, like data.access_token as token. Later steps can use {{token}} in their URL, headers or body. Saved values can't change which host a step calls.
Are my API keys safe?
Headers are stored with the monitor and visible to everyone in your workspace, so use a read-only or dedicated key.
Do HTTPS APIs get SSL checks too?
Yes. API monitors record the certificate expiry and warn you 14, 7 and 1 day before it lapses.

Set up API monitoring in under a minute

Included on the Free plan. No card needed.

Create a free account